AI Security
CISA Admin Leaked AWS GovCloud Keys on Github
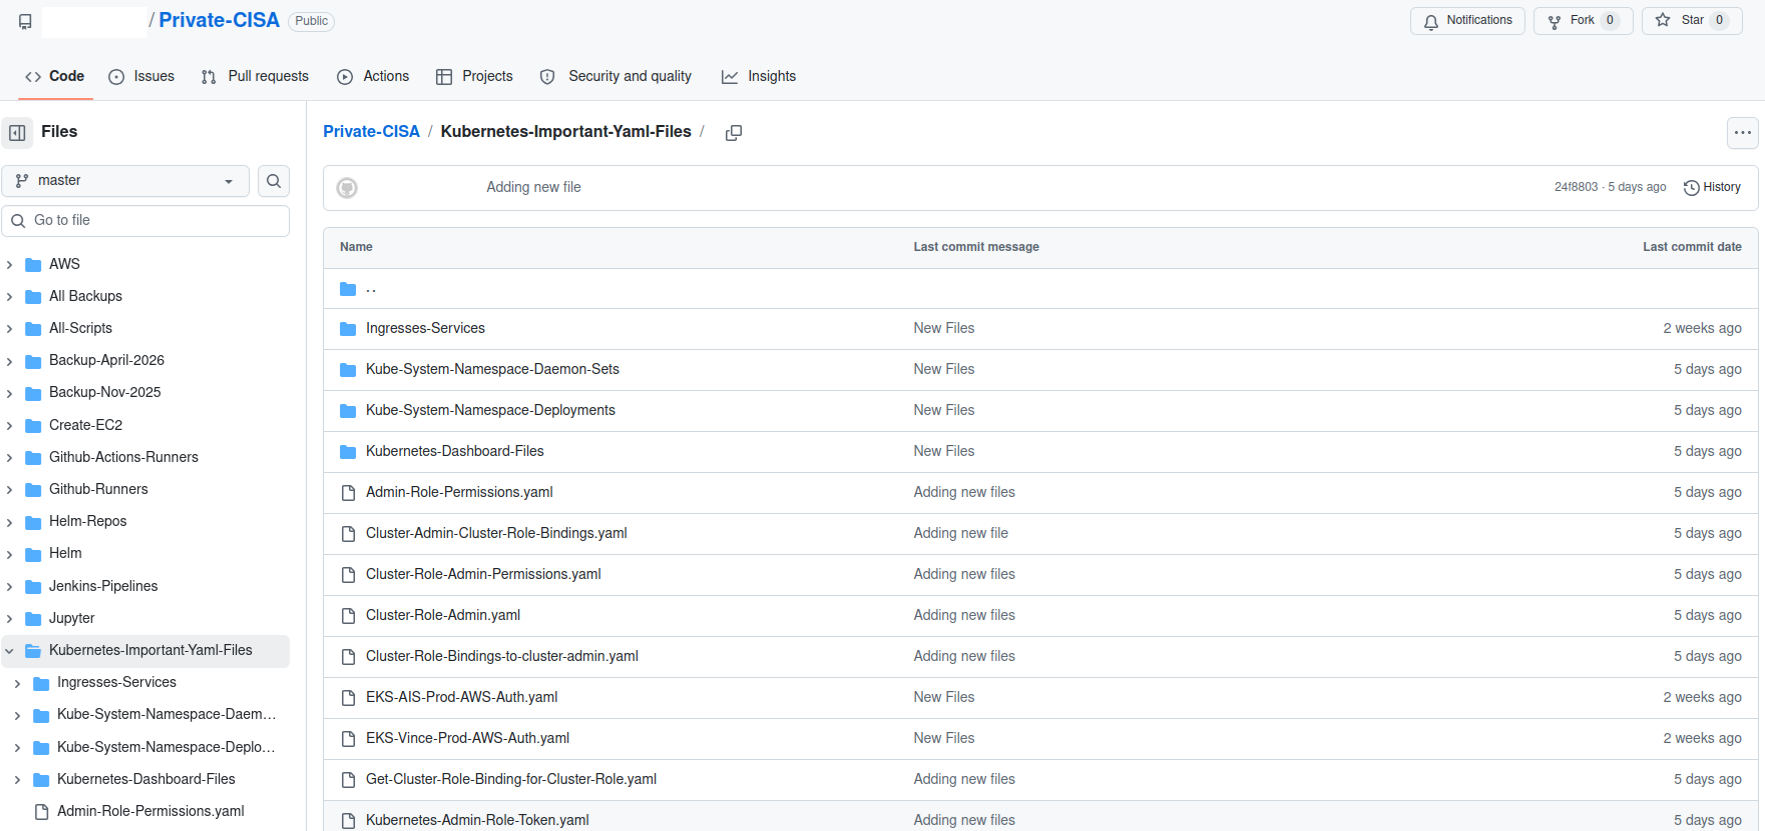
Until this past weekend, a contractor for the Cybersecurity & Infrastructure Security Agency (CISA) maintained a public GitHub repository that exposed credentials to several highly privileged AWS GovCloud accounts and a large number of internal CISA systems. Security experts said...
KoS
Krebs on Security
Source
Krebs on Security
AI Analysis
Generated insight by OnAirToday AI
This incident highlights the critical need for robust access control and security best practices, even within government agencies. The exposure of highly privileged AWS GovCloud keys and internal system details underscores the significant risks associated with mishandling sensitive credentials in cloud environments.
Powered by AI • Not a substitute for human analysisMore Insights →
Share
Filed under:AI Security

Comments
Keep comments relevant and respectful. No links, advertising, self-promotion, or spam.