Who Operates the Badbox 2.0 Botnet?
Inter-botnet warfare reveals new clues about the mysterious operators behind the widespread Badbox 2.0 malware.
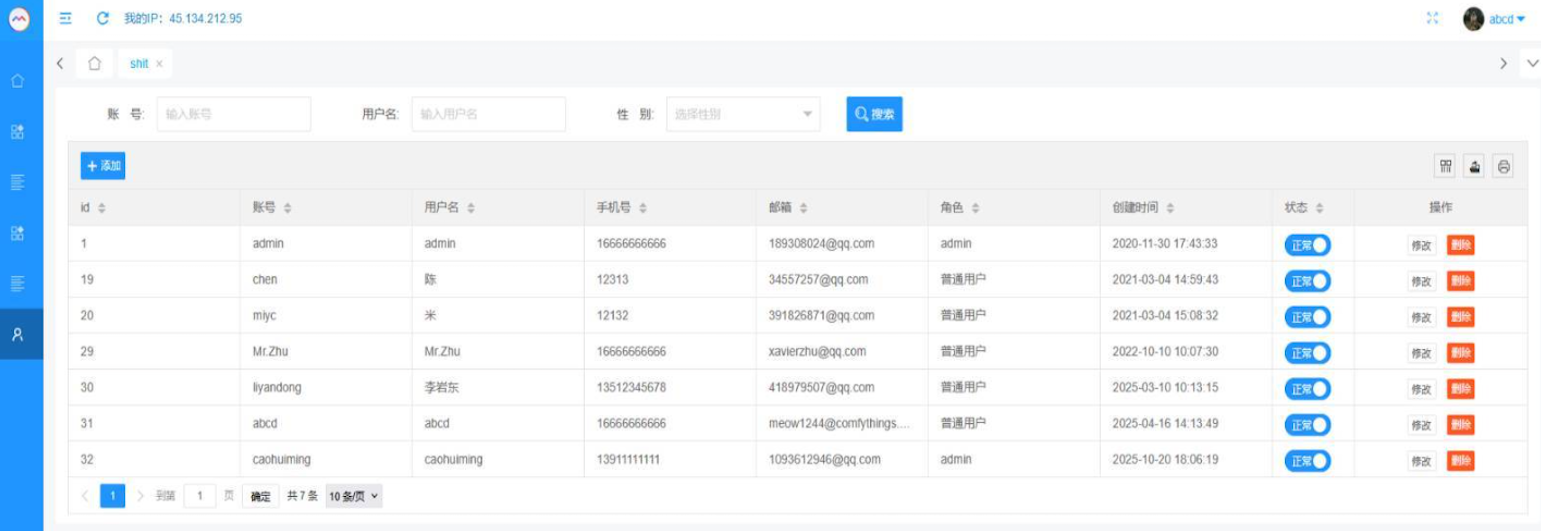
The cybercriminals in control of Kimwolf -- a disruptive botnet that has infected more than 2 million devices -- recently shared a screenshot indicating they'd compromised the control panel for Badbox 2.0, a vast China-based botnet powered by malicious software that comes pre-ins...
Krebs on Security
Source
Generated insight by OnAirToday AI
The collision of two massive botnet syndicates reveals critical vulnerabilities in global supply chain security for consumer hardware. By monitoring the internal communications of cybercriminals, researchers can now trace the origins of pre-installed malware that has compromised millions of devices worldwide.
Comments
Keep comments relevant and respectful. No links, advertising, self-promotion, or spam.